Provably Fair Gaming: How Crypto Casinos Let You Verify Each Result
If you have ever lost a few spins in a row and quietly wondered whether the game was rigged, you are not alone. Provably fair systems hand you the math and let you check the result yourself, with no trust in the operator required. This approach started in the Bitcoin gambling scene around 2012 and has since spread across most crypto casinos. The house edge and payout rates stay exactly what they were. What changes is that you get a way to confirm that the outcome you got is the outcome the math actually produced, with nobody quietly editing the result after you placed your bet. The verification process takes about a minute once you know where to click.
What “provably fair” actually means
A provably fair game proves two things to you:
- The casino committed to a result before you bet, so it could not change it after seeing your wager.
- The result was influenced by your input too, so the casino could not pick a number you had no say in.
Both of those rely on a piece of cryptography called a hash function. A hash takes any input and turns it into a fixed string of characters. The same input always gives the same hash. Change one letter and the hash looks completely different. And you cannot run it backwards: given the hash, you cannot figure out the original input. That one-way property is what makes the whole trick work.
The specific algorithm you will see most often is HMAC-SHA256. It combines the server seed, your client seed, and a nonce into a single value that determines the round’s outcome. HMAC is a standard way of mixing two inputs so the result is unpredictable even if parts of the input are known, and the underlying hash is a widely trusted building block used across the broader crypto ecosystem. This is not casino-specific technology, which is partly why it became the default.
The mental model I use is a locked box. The casino puts its secret in the box and shows you the box before you bet. After the round, it hands you the key. You open the box and confirm the secret inside matches what was locked up all along.
How it works, step by step
Most provably fair games follow the same loop. The exact wording differs between casinos, but the bones are the same.
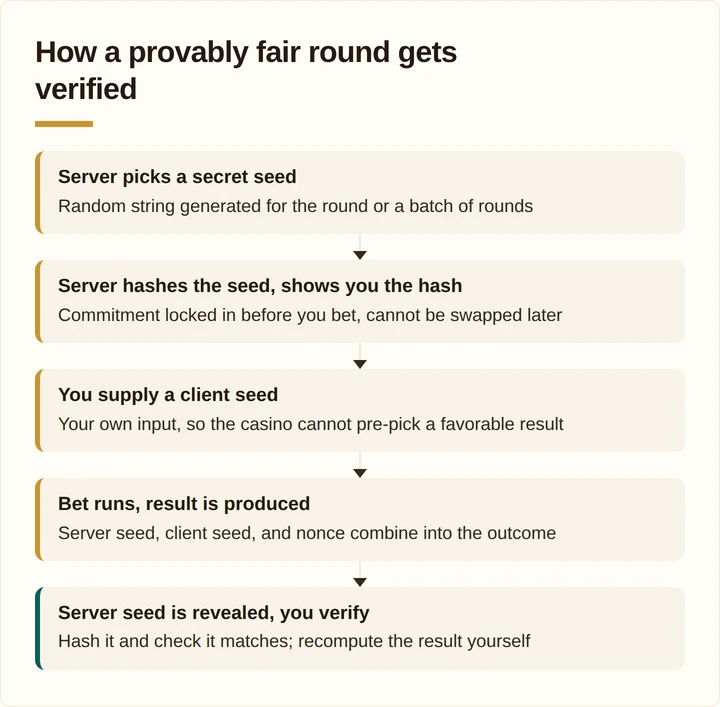
- The server picks a secret seed. This is a random string the casino generates for the round (or for a batch of rounds).
- The server hashes that seed and shows you the hash. You see the hash before you bet. You cannot reverse it, but the casino is now locked in. It cannot swap the seed later without the hash no longer matching.
- You provide a client seed. This is your own input. Some casinos auto-generate it in your browser, others let you type whatever you want. Because you control it, the casino cannot have pre-computed a result it likes.
- You place your bet. The round runs.
- The game combines server seed, client seed, and usually a nonce (a counter that increases each bet) to produce the outcome. A roll, a card, a crash multiplier, whatever the game is.
- The casino reveals the original server seed. Now you can do two checks yourself.
To verify it yourself:
- Hash the revealed server seed and compare it to the hash you were shown in step 2. If they match, the casino did not change the seed.
- Feed the server seed, your client seed, and the nonce into the same formula the game used. If you get the same result you were paid on, the round was honest.
Most casinos publish their exact algorithm and a verification page so you do not have to write code. You can also paste the values into independent third-party verifiers.
A worked example (illustrative values, not a real round)
A made-up example computed locally with standard Python libraries demonstrates the process. These seeds and hashes are fabricated purely for demonstration. They do not come from any real casino round or game.
| Step | Value |
| Server seed (secret) | f3a9c1e7b8d2a04f6c91e5b7d3a8f210c4e9b6a1d7f0328e5c6b9a1d4f7e0213 |
| SHA-256 commitment shown before betting | a1998c24140c308631f18508db0210beccece75831a3af3fce05479245dbdfc7 |
| Client seed | player-rolls-2026 |
| Nonce | 1 |
| HMAC-SHA256(server_seed, “player-rolls-2026:1”) | 004f0eb59ae1481cf547efae3bab7714a1a6c5586b0e38324e18488269706e2e |
To derive the game result, you take the first 8 hex characters of that HMAC output (004f0eb5), interpret them as an integer, apply modulo 10000, and divide by 100. That gives a roll of 11.09 on a 0.00–99.99 scale.
I ran this through Python’s hashlib and hmac modules to confirm every step. You can reproduce it with any free hash calculator online in under a minute. The specific number matters less than the fact that the entire chain is transparent and repeatable.
The nonce is what makes this system practical for real play. Without it, the casino would need a fresh server seed for every single bet, which would mean showing you a new commitment hash before each round and making the verification process far more cumbersome. Instead, one server seed can cover thousands of consecutive bets. Each bet increments the nonce by one, so the same seed pair never produces the same result twice. When you verify a round, you simply check that the nonce matches the bet number you were shown at the time. This batching mechanism is standard across provably fair platforms and is why you can play hundreds of rounds under a single seed pair while still having every result independently checkable.
Verifying dice, crash, and roulette-style games
The seed pipeline works the same way across these game types. What changes between game types is only the last step: how the raw hash output gets turned into a game result. That last step is called the output mapping, and once you can read it, you can verify any provably fair game on the site, not just the one you happened to start with.
Dice and roll games are the baseline case, and the worked example above already walked through it. Take the leading hex characters of the HMAC output, convert them to an integer, apply a modulo to squeeze the number into the game’s range, then scale it to the display format. A 0.00–99.99 roll and a 1–100 roll are the same operation with different arithmetic on the end. If you can verify one dice round, you can verify every dice round on every platform that publishes its range.
Crash games reuse the identical seed pipeline but swap the mapping. Instead of a bounded roll, the game converts the hash into a floating-point number between 0 and 1, then feeds that float into a formula shaped to produce a multiplier. One common approach takes the inverse of the float — small floats produce large multipliers, large floats produce small ones — and then applies a floor and an edge adjustment. That edge parameter is where the house margin lives. In common implementations, a fixed share of outcomes resolve at exactly 1.00x, which is the instant crash point — anyone who has not already cashed out at that moment loses their full stake. The game is not malfunctioning when that happens. It is the formula doing precisely what it was written to do.
Because the edge is baked into the mapping rather than bolted on afterward, two crash games can use the same seeds and the same hash and still produce different multipliers. The seeds determine the raw number. The formula determines what that number is worth. When you verify a crash round, you are checking both: that the seed was the committed one, and that the published formula turns that seed into the multiplier you were paid on.
Roulette-style and other multi-outcome games take a third route. The hash output is reduced to a single slot out of N. For a European wheel, N is 37 — the pockets 0 through 36. The modulo operation picks one, and that is your number. The mapping itself carries no house edge. Every pocket is equally likely from the hash’s point of view. The edge in roulette comes from the payout table, not the selection: a straight-up bet pays 35 to 1 against 37 possible outcomes, and that gap is the margin. This is worth separating in your head, because it means a roulette round can be perfectly fair at the selection stage and still be a losing proposition over time. Fairness and profitability are different questions.
Here is the general lesson. The verification method never changes. You recompute the HMAC from the revealed server seed, your client seed, and the nonce, then compare your result to what the game showed you. That procedure is identical whether you are checking a dice roll, a crash multiplier, or a roulette pocket. Only the output mapping differs, and on most provably fair platforms the mapping is published alongside the game. Learn to read one mapping and you have learned to read them all. The cryptography does not care what game you are playing. It only cares that the inputs match.
Provably fair vs audited RNG (eCOGRA/GLI)
Both systems get called “fairness checks” and they are actually quite different. Provably fair is player-driven verification of a single round. Audited RNG is institutional certification of a whole game over millions of rounds.
Third-party labs like eCOGRA and GLI hold ISO/IEC 17025 accreditation. They certify randomness by running statistical tests across millions of simulated rounds to check for bias or patterns. Regulators then license operators based on meeting those standards. This is a centralized model. You trust the lab, the regulator, and the operator’s compliance.
Provably fair inverts that. There is no third party in the middle. The math itself is the witness, and you are the auditor. The two models answer different questions and rarely overlap in practice.
| Provably fair | Audited RNG (eCOGRA/GLI) | |
| Trust model | Player verifies each round directly | Centralized certification by accredited labs |
| Who verifies | You, with a hash calculator | The lab, over millions of simulated rounds |
| When you can check | After every single bet | When the certification is issued (periodically) |
| What it proves | The committed seed was used honestly | The RNG is statistically unbiased |
| Typical use | Crypto-native casinos | Regulated operators (UK, MGA, US states) |
Regulated operators under UK, Maltese, or US-state jurisdictions rely on GLI-certified RNG almost exclusively. Crypto-native operators, often under Curacao or Antigua licensing or none at all, use provably fair almost universally. The two ecosystems have minimal overlap. If you play at a regulated casino, you will rarely see provably fair tools. If you play at a crypto casino, you will rarely see GLI certificates. For more on how the crypto side compares to a regular fiat account day to day, see our look at crypto vs fiat casinos.
Each system has a blind spot the other covers. Provably fair does not prove the underlying randomness is statistically sound. Audited RNG does not prove the operator did not tamper with a specific round after you bet. Neither is “better” in the abstract. They serve different regulatory and trust environments.
If a casino advertises “provably fair” prominently, it is almost certainly crypto-native and not built to satisfy a regulator like the UK Gambling Commission or the Malta Gaming Authority. If a casino instead cites a specific license number and an RNG test certificate from a named lab, it is operating in the opposite model. Neither absence alone proves the operator is untrustworthy, but knowing which model a site uses tells you which questions are worth asking. For a provably fair site, ask to see the verification tool and test a round yourself. For a licensed site, ask for the certificate number and look it up with the regulator. Matching your scrutiny to the model is the fastest way to separate marketing from substance.
What it protects you from, and what it doesn’t
Provably fair catches real problems, like a casino swapping a result after the fact, but it is sold harder than it deserves sometimes. Keep both columns in mind.
What it does protect you from:
- The operator changing a result after seeing your bet.
- The operator feeding you a rigged sequence it generated in advance.
- Silent tampering on individual rounds, which you can catch by verifying.
What it does not do:
- It does not remove the house edge. A provably fair coin flip can still pay less than even money. The math is honest; it is also tilted toward the house, by design. Always check the actual odds.
- It does not prove the casino will pay you. Fair results mean nothing if the operator refuses a withdrawal. Solvency and licensing are separate questions.
- It does not audit the random number generation quality on its own. It proves the committed seed was used. Whether the seed was drawn from genuinely good randomness is a related but different concern, which is why third-party testing still matters.
- It only helps if you actually verify. Almost nobody does. The protection is real but mostly theoretical unless you spot-check.
The system is built so that cheating would eventually get caught by someone who checks. Its deterrent value comes from the fact that it is checkable at all, and it does not require constant verification by every player to be effective.
Independent bodies like eCOGRA audit game randomness and payout behaviour, and regulators such as the UK Gambling Commission set rules on how games must behave regardless of the underlying tech. Provably fair sits alongside those as one more layer, addressing a different part of the trust problem.
FAQ
Do I need to understand cryptography to benefit from this? No. You benefit from the design existing even if you never run a check. If you want to verify, the casino usually gives you a one-click tool. Copy the seeds in, compare the output.
Why does the casino reveal the server seed only after the round? Because if you saw the seed before betting, you could calculate the result and only bet on winners. Revealing it afterward, while having shown the hash beforehand, is what keeps both sides honest.
Can I change my client seed? On most platforms, yes, and it is a good habit. Rotating your client seed means you are not stuck with a value the casino could have planned around.
Is provably fair the same as “licensed and safe”? No. They answer different questions. Provably fair answers “was this result honest.” Licensing answers “is this operator allowed to run, and will it pay.” You want both. If you ever feel your play is slipping out of control, support services like GamCare exist regardless of how fair the games are.
Does this work for slots from big studios? Rarely, and only in a limited sense. Provably fair is most common in crypto-native games (dice, crash, plinko). Branded slots from major providers run on the studio’s own RNG and are checked through third-party audits.
Why HMAC-SHA256 specifically? SHA-256 is a widely trusted, standardized hash with no known practical collisions, and HMAC adds a keyed layer that prevents someone from predicting the output even if they know part of the input. It is also publicly documented and easy to verify with free tools, which is exactly what a player-driven verification model needs. Casinos did not invent it. They adopted a hash standard already used across banking and software security.
Does provably fair replace RNG certification like eCOGRA or GLI? No. Provably fair proves the committed seed was used honestly for a given round. RNG certification proves the underlying generator is statistically unbiased across millions of rounds. A game could be provably fair and still use poor randomness, or certified and still theoretically tampered with on a single round. They cover different failure modes, which is why regulated and crypto-native operators tend to pick one model or the other rather than both.
Provably fair gives you a receipt you can verify. It does not change the odds, and it does not vouch for the operator’s integrity outside the game logic. Treat it as one useful signal among several, not as proof that you are going to win.